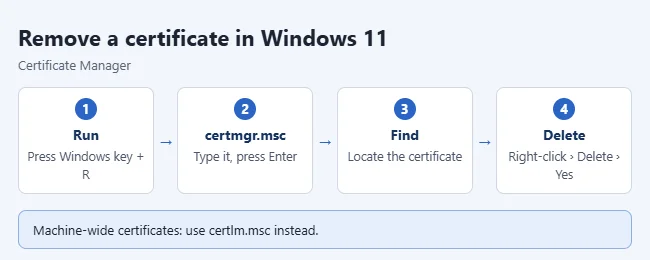
To remove a certificate in Windows 11, press Windows key + R, type certmgr.msc, and press Enter. Find the certificate in the left pane, right-click it, and choose Delete, then Yes. For certificates installed for the whole computer, open certlm.msc instead.
These steps apply to all current Windows 11 releases. They also match Windows 10, which reached end of support on October 14, 2025. The methods follow Microsoft’s documentation on viewing certificates with the MMC snap-in and Certificate Manager, exporting a certificate, the PowerShell Certificate provider, and the certutil command.
User Certificates vs. Computer Certificates
A certificate is a small file that proves the identity of a website, a person, a device, or a piece of software. Windows keeps certificates in separate stores. The Current user store belongs to your account only, and you open it with certmgr.msc. The Local computer store applies to all users on the device, and you open it with certlm.msc. There is also a store for each service. Microsoft notes that if you aren’t an administrator, you can manage certificates only for your own user account.
The same certificate can sit in both stores, so check both if you are trying to get rid of it completely. Inside each store, certificates are grouped into folders:
| Folder | What it holds | Risk of deleting |
|---|---|---|
| Personal | Certificates issued to you or this PC, often with a private key (email signing, VPN, Wi-Fi, smart card) | Low if you know what it is, but the app that uses it stops working |
| Trusted Root Certification Authorities | The top-level authorities Windows trusts for websites, updates, and signed software | High |
| Intermediate Certification Authorities | Authorities that link a website’s certificate back to a trusted root | High |
| Trusted Publishers | Software publishers you chose to trust | Medium |
| Untrusted Certificates | Certificates Windows has been told to reject | Deleting one can make Windows trust it again |
To tell certificates apart, look at the Issued To, Issued By, Expiration Date, and Intended Purposes columns. Several certificates can share a name, so the thumbprint (covered below) is the reliable way to identify one.
Before You Delete Anything: Back Up the Certificate
Certificates are used as credentials by apps and services, so a certificate that looks unused may still be needed. Removing the wrong root or system certificate can break websites, Windows Update, VPN connections, Wi-Fi sign-in, and work or school sign-in. Remove only certificates you installed yourself, ones left behind by software you have uninstalled, or ones your IT department tells you to remove. Leave anything issued by Microsoft or deployed by your organization alone, and never delete certificates in bulk.
Exporting a copy first lets you import it again later:
- Open Certificate Manager and select the certificate.
- On the Action menu (or by right-clicking), point to All Tasks, then select Export.
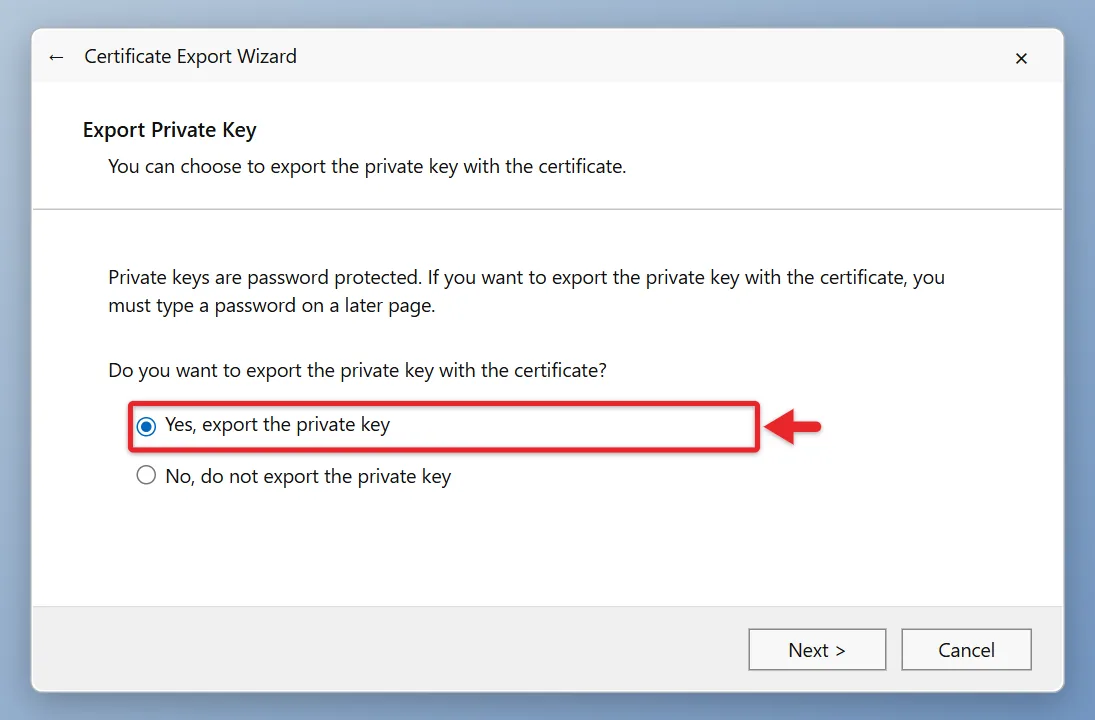
- Follow the Certificate Export Wizard. If you need the private key, choose Yes, export the private key and set a password.
- Choose a file name and location, then select Finish.
You now have a backup file, and the certificate stays in the store. A file exported with the private key is a password-protected PKCS #12 file (usually ending in .pfx). A file without the key (usually .cer) holds only the public part, which is enough for root and intermediate certificates. Keep the .pfx file somewhere safe, because anyone with the file and password can use your identity.
The Yes, export the private key option appears only if the key was marked as exportable and you have access to it. If it is greyed out, the key can’t be backed up, and deleting the certificate together with its key can’t be undone. Ask whoever issued it whether you can get a new one before you remove it.
How to Remove a Certificate for Your User Account
- Press Windows key + R to open Run.
- Type certmgr.msc and press Enter. The Certificates – Current User window opens.
- In the left pane, expand the folder the certificate is in, such as Personal > Certificates. The certificates in that folder appear on the right.
- Double-click the certificate and check Issued to, Issued by, and Valid from to confirm it is the right one. Close the window.
- Right-click the certificate and choose Delete.
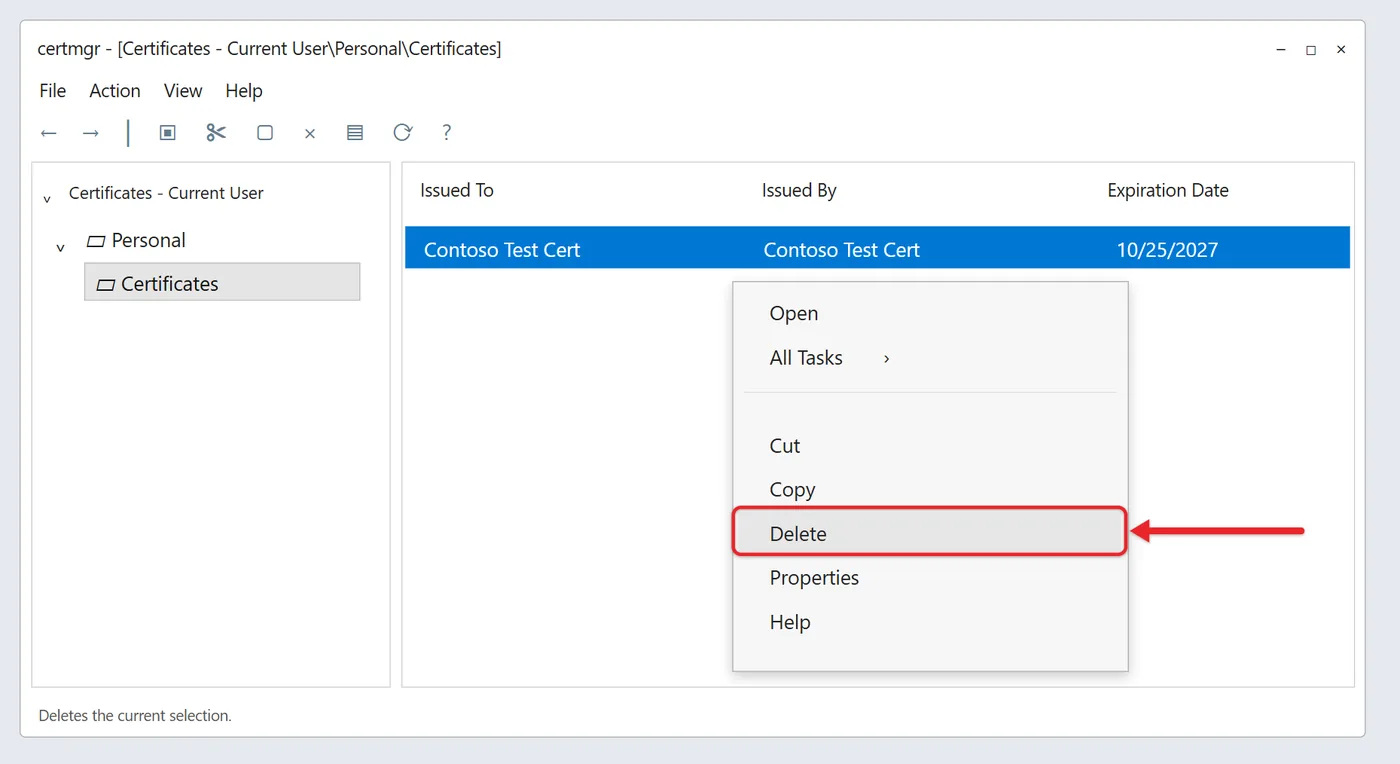
- Select Yes to confirm.
The certificate disappears from that folder for your account only. Other accounts on the PC are not affected.
How to Remove a Certificate for the Whole Computer
- Press Windows key + R.
- Type certlm.msc and press Enter. Select Yes if Windows asks for administrator permission.
- Under Certificates – Local Computer, expand the folder that holds the certificate.
- Right-click the certificate, choose Delete, and confirm with Yes.
The certificate is removed from the local computer store, which applies to every user and service on the PC. The change takes effect right away.
How to Distrust a Certificate Without Deleting It
If you’re not sure a certificate is safe to remove, turning off its purposes is a reversible middle step. Microsoft’s page on modifying the properties of a certificate describes this option.
- In certmgr.msc or certlm.msc, right-click the certificate and choose Properties.
- Select Disable all purposes for this certificate. To turn off only some uses, select Enable only the following purposes and clear the boxes you don’t want.
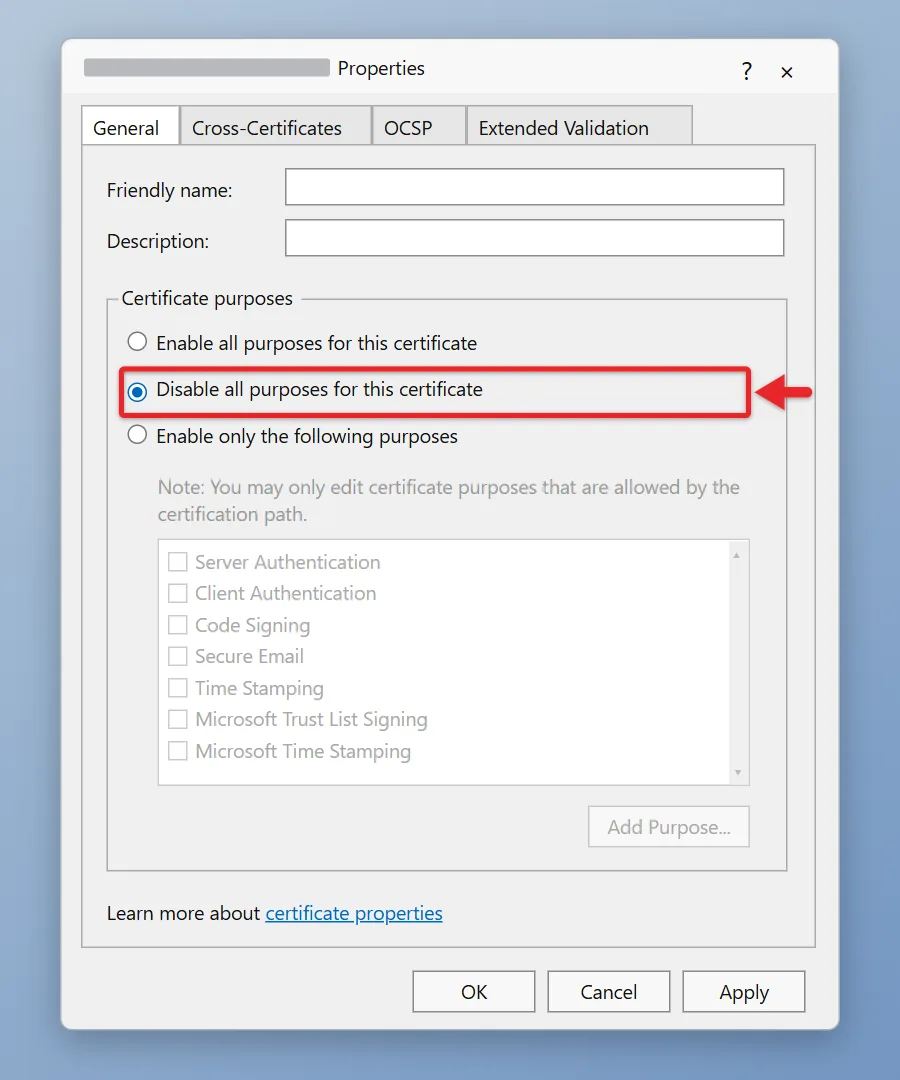
- Select OK.
The certificate stays in the store but Windows no longer trusts it for the purposes you turned off. To undo it, return to Properties and select Enable all purposes for this certificate.
How to Use the MMC Snap-in Instead
- Open Run, type mmc, and press Enter.
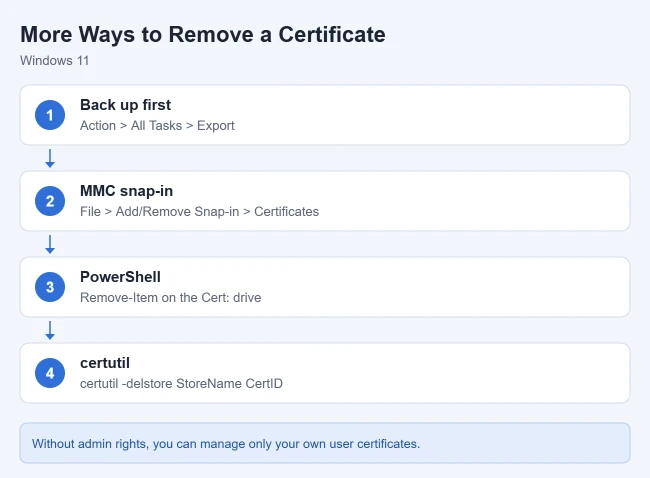
- Select File > Add/Remove Snap-in.
- Choose Certificates, select Add, then pick My user account, Computer account, or Service account.
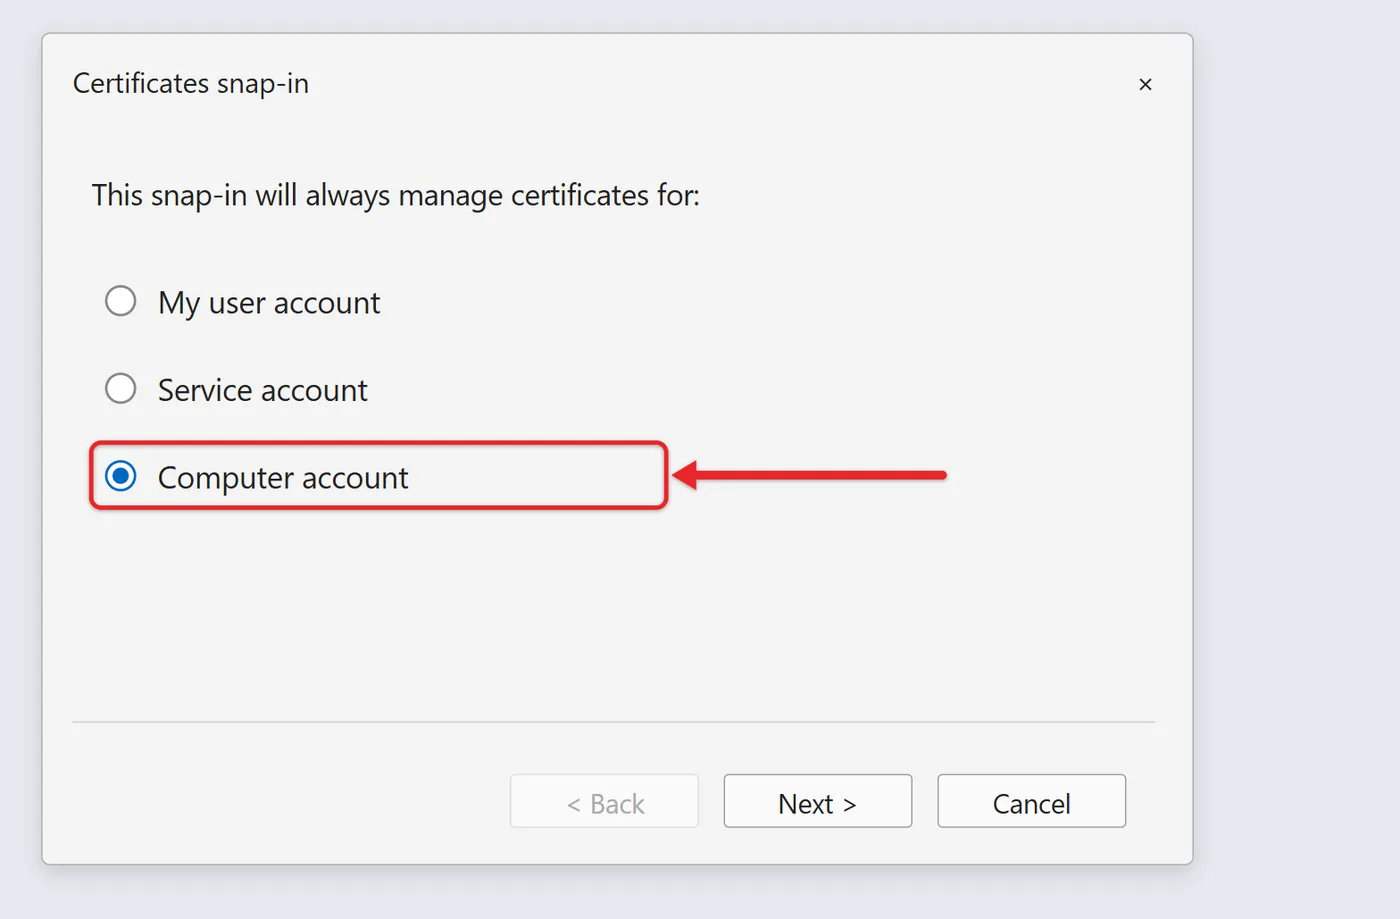
- Finish the wizard and select OK.
- Expand the certificate store under Console Root, find the certificate, and delete it.
You get the same delete option, plus access to service account stores. You can save the console with File > Save to reuse it later.
Windows also has an older route through Internet Options. Press Windows key + R, type inetcpl.cpl, press Enter, open the Content tab, and select Certificates. Pick a tab such as Personal, select the certificate, and select Remove. This list shows your user certificates, so certmgr.msc is the clearer choice for most people.
How to Remove a Certificate With PowerShell
Windows PowerShell exposes your certificate stores as the Cert: drive. Per Microsoft, Remove-Item deletes the certificate at the path you give it, using the certificate’s thumbprint. Microsoft’s example removes a certificate from the local computer’s CA store:
Remove-Item Cert:\LocalMachine\CA\5DDC44652E62BF9AA1116DC41DE44AB47C87BDD0This leaves the associated private key in place. Adding the -DeleteKey parameter deletes the private key too. Replace the thumbprint with the one for your certificate, and run PowerShell as an administrator for LocalMachine stores. To see what would happen without deleting anything, add -WhatIf to the end of the command first. WhatIf and Confirm are among the few parameters Remove-Item supports on the Cert: drive.
If you know the certificate’s name but not where it is, Get-ChildItem Cert:\CurrentUser -Recurse | Where-Object Subject -like "*Contoso*" searches every folder of your user store. Swap in part of your certificate’s name, and use Cert:\LocalMachine for the computer store. The PSParentPath in the output shows which folder it is in.
How to Find a Certificate’s Thumbprint
PowerShell and certutil both need the thumbprint, a 40-character ID that is unique to each certificate. To copy it:
- Open certmgr.msc or certlm.msc and double-click the certificate.
- Select the Details tab.
- Scroll down and select Thumbprint. The value appears in the box below the list.
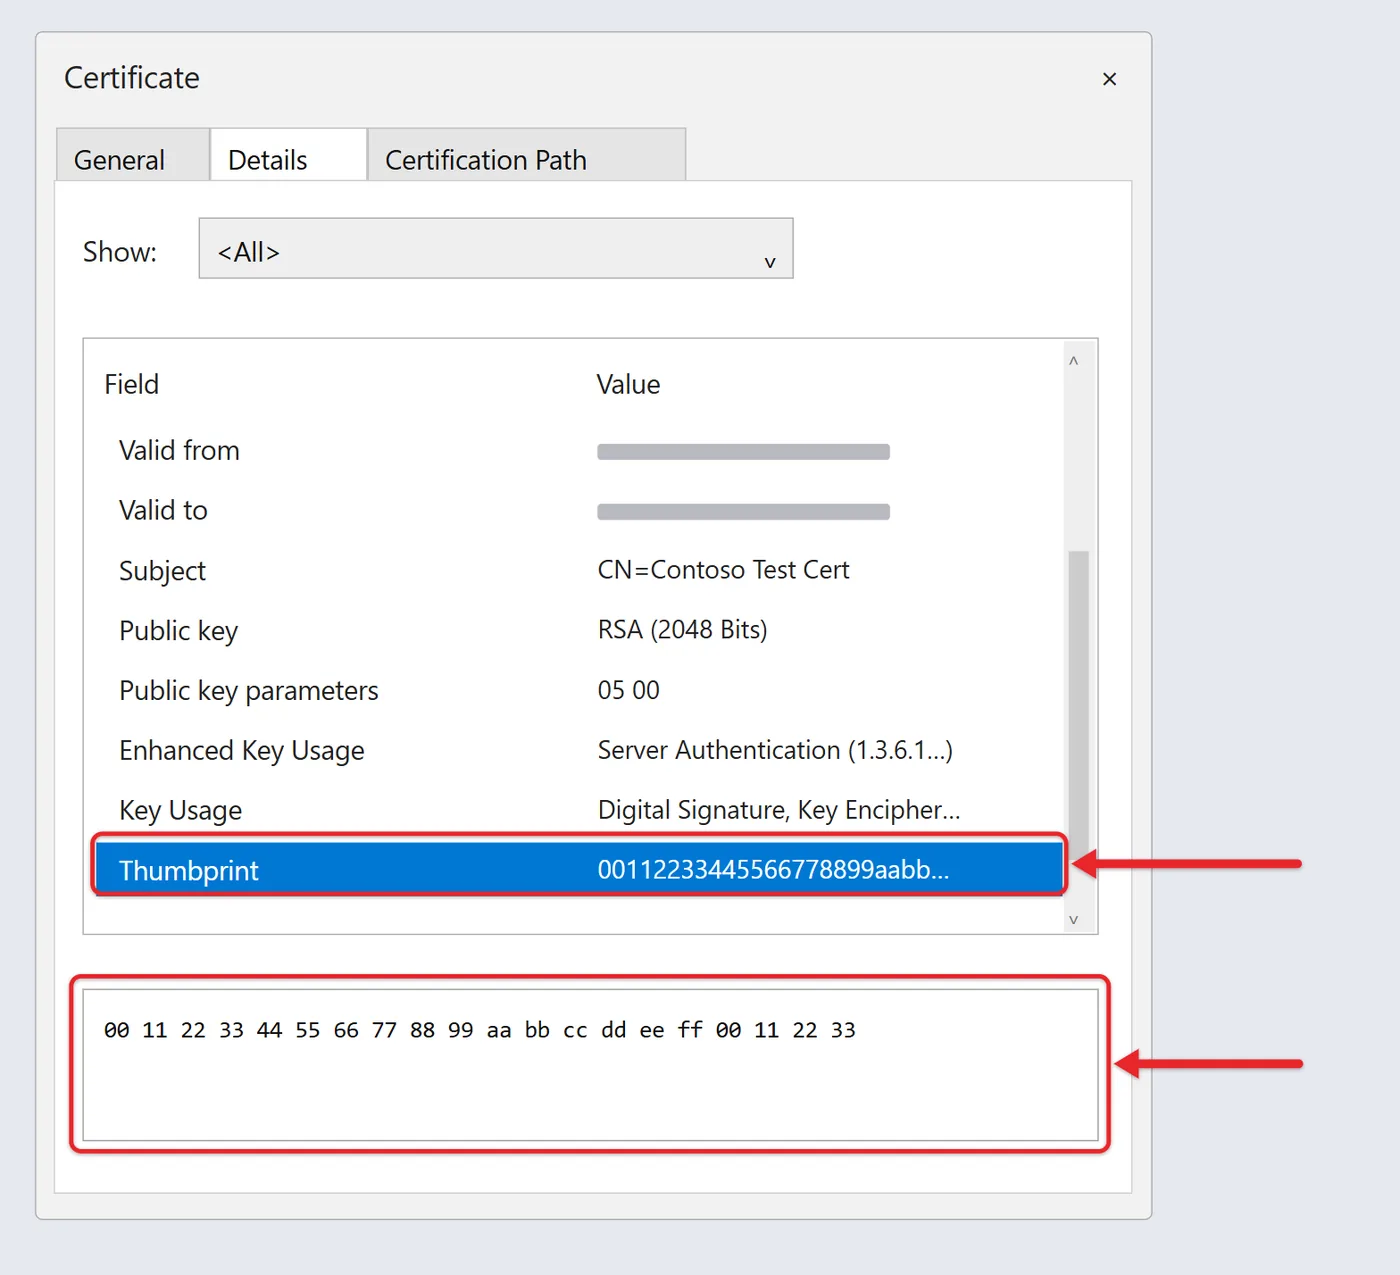
- Select the value, press Ctrl + C, and paste it into your command. Remove any spaces.
In PowerShell, Get-ChildItem Cert:\CurrentUser\My lists the thumbprint and subject of every certificate in your Personal store. Change the path to Cert:\LocalMachine\My for the computer store.
How to Remove a Certificate With certutil
The certutil -delstore command deletes a certificate from a store. The syntax is certutil -delstore StoreName CertID, and the CertID can be the certificate’s thumbprint or serial number. Common store names are My (Personal), Root (Trusted Root Certification Authorities), and CA (Intermediate Certification Authorities). Run certutil -store My first to list what is in a store.
For example, open Command Prompt as an administrator and run certutil -delstore My 5ddc44652e62bf9aa1116dc41de44ab47c87bdd0 to remove that certificate from the computer’s Personal store. Add -user to work on your own account’s store instead: certutil -user -delstore My 5ddc44652e62bf9aa1116dc41de44ab47c87bdd0. Replace the thumbprint with your own. Certutil is meant for developers and IT administrators, so export a backup first.
How to Confirm It Worked or Put a Certificate Back
Press F5 in Certificate Manager to refresh the list and make sure the certificate is gone from that folder. In PowerShell, Get-ChildItem Cert:\ -Recurse | Where-Object Thumbprint -eq "YOURTHUMBPRINT" checks both stores at once. No output means the certificate is gone. Then close and reopen any browser or app that used it, because some apps keep the old result in memory.
To restore a certificate from your backup:
- Open the same store you removed it from and select the folder it came from.
- On the Action menu, point to All Tasks, then select Import.
- In the Certificate Import Wizard, select Browse and pick your .pfx or .cer file.
- For a .pfx file, enter the password you set during export.
- Choose Place all certificates in the following store, confirm the folder, and select Finish.
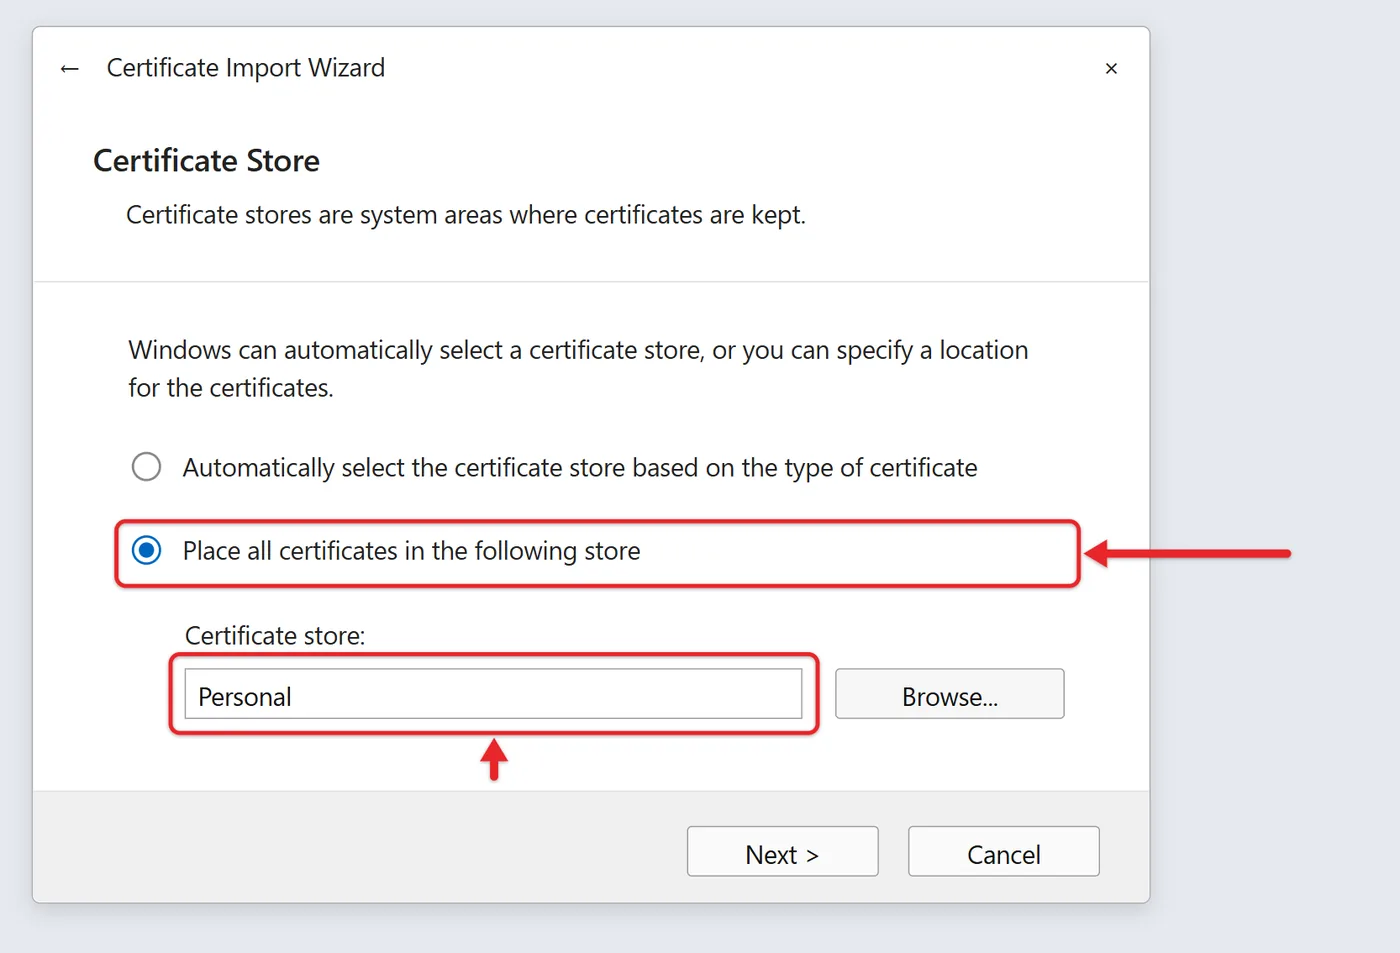
Microsoft’s import steps also warn to import certificates only from sources you trust.
When Delete Is Gray or Access Is Denied
Delete is greyed out or you see “Access is denied.” You are in the local computer store without administrator rights. Open certlm.msc from an administrator account, or ask the person who manages the PC. A certificate pushed by a work or school organization may be locked by policy.
The certificate came back. Windows downloads Microsoft’s list of trusted root certificates automatically, so a public root you delete can be added again the next time a site or app needs it. Microsoft’s certificate trust overview says this automatic update can be turned off but isn’t recommended. Group Policy, device management, a smart card such as a CAC, or the app that installed the certificate can also put it back. Remove or reconfigure the source first.
A website still loads after you removed its certificate. Check the other store (user or computer), then restart the browser. Firefox keeps its own list of trusted authorities, and Chrome also uses its own root list for public certificate authorities, so removing a public root from Windows may not change what those browsers trust.
Something stopped working after a deletion. Import your backup as shown above. If you have no backup of a public root, Windows usually adds it back automatically when a site or app needs it. For a work certificate, contact your IT department.
Certificate Questions
Why can’t I delete a certificate in certlm.msc?
Changes to the local computer store need administrator rights. Without them, you can manage certificates only for your user account in certmgr.msc.
Does deleting a certificate delete its private key?
It depends on the tool. In PowerShell, Remove-Item leaves the private key unless you add -DeleteKey. Export a backup with the private key first if you might need it again.
Do I need to restart Windows after removing a certificate?
No. The store changes right away. Restart the browser or app that used the certificate so it stops using a cached copy.
Is it safe to delete expired certificates?
Expired certificates in your Personal folder are usually safe to remove after a backup. Leave expired certificates in the root folders alone unless your IT department says otherwise, because Windows manages those lists itself.
Can I get back a certificate I deleted without a backup?
Only in some cases. Public root certificates usually return through Windows’ automatic root updates. A personal certificate with a private key can’t be recovered, so you would need to request a new one from whoever issued it.
For more Windows security help, browse the Windows security articles, or learn how to enable Secure Boot in Windows 11 and how to open the Run command in Windows 11.

Matthew Burleigh is the founder, head writer, and editor of Solve Your Tech, which he launched in 2012. He has written technology tutorials since 2008 and worked in IT since 2003, including small-business support, IT management, and consulting. He holds Bachelor’s and Master’s degrees in Computer Science from Arizona State University.
Matthew writes practical guides for Windows, iPhone and iPad, Microsoft Office, Outlook, Google apps, and Android. Solve Your Tech’s guides are checked step by step against the device or app maker’s own documentation and tested on his own devices whenever he has the hardware or software, with clear steps, sources, and update dates.
Read more about Matthew and how Solve Your Tech writes and updates its guides, or report a correction.