To disable Credential Guard in Windows 11 on a PC you manage yourself, set the LsaCfgFlags registry value to 0 under HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Lsa and HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\DeviceGuard, then restart. If Group Policy turned it on or it was enabled with a UEFI lock, use the matching method below instead. You don’t need to disable Hyper-V.
This covers Windows 11, version 22H2 and later, where Microsoft turns Credential Guard on by default for eligible Enterprise and Education PCs. The steps follow Microsoft’s Configure Credential Guard page, checked in October 2026. Windows 10 reached end of support on October 14, 2025.
Credential Guard should stay on. Turn it off only when a specific app, network sign-in or virtualization tool is confirmed to need it off, on a PC you manage. On a work or school PC, your IT team manages this setting, so ask them instead of changing it.
What Credential Guard Protects
Microsoft’s Credential Guard overview says it protects NTLM password hashes, Kerberos Ticket Granting Tickets and credentials that apps store as domain credentials. It keeps them in virtualization-based security (VBS), an isolated area that the rest of Windows can’t read, so even malware with administrator rights can’t steal them for “pass the hash” attacks.
Microsoft supports it on Enterprise and Education, not Home or Pro, although a Pro PC that once ran it on an Enterprise license can keep it on. On other Home or Pro PCs, Credential Guard probably isn’t what is blocking your app.
Check Whether Credential Guard Is Running
- Search Start for msinfo32.exe and open System Information.
- Select System Summary and find Virtualization-based Security Services Running. Check whether it includes Credential Guard. Record the result before changing anything.
- If Credential Guard isn’t listed, it isn’t running and isn’t causing your problem. Look at the app’s exact error message instead.

For a read-only check from the command line, open Windows PowerShell as administrator and run:
(Get-CimInstance -ClassName Win32_DeviceGuard -Namespace root\Microsoft\Windows\DeviceGuard).SecurityServicesRunningMicrosoft’s Credential Guard configuration guide says 1 means Credential Guard is running and 0 means it isn’t. The command can list several numbers. Microsoft’s memory integrity page explains that 2 means memory integrity is running, so a 2 without a 1 means Credential Guard is off.
Separate Credential Guard From Other Protections
VBS is the isolated environment used by several security features. Memory integrity protects kernel code and is a separate feature from Credential Guard. Microsoft’s VBS explanation describes that relationship. Switching off memory integrity alone is not a reliable Credential Guard procedure.
Removing Hyper-V affects other features too. Our Windows 11 Hyper-V guide explains that feature. Turning off firmware virtualization, clearing the TPM or disabling Secure Boot isn’t part of disabling Credential Guard. Microsoft warns that clearing the TPM permanently loses data that VBS features protect.
Before You Change Anything
- Confirm the need. Check the app maker’s current guidance for your exact version. Microsoft’s known-issues page lists VMware Workstation among products that have reported problems, but newer versions may differ. Record the error so you can compare afterward.
- Back up the registry keys. Open Registry Editor, select each key below, and use File > Export, following Microsoft’s registry backup guide. Note whether each value existed and what it was.
- Find out what controls the setting. Intune, Group Policy, the registry or Windows’ default can turn it on. Use only the matching method.
Method 1: Group Policy
Use this when Group Policy turned Credential Guard on without a UEFI lock. Local Group Policy Editor is included in Windows 11 Pro, Enterprise and Education.
- Press Windows + R, type gpedit.msc, and press Enter. See how to open Local Group Policy Editor if it doesn’t open. The editor window opens.
- Go to Computer Configuration > Administrative Templates > System > Device Guard. The Device Guard settings appear on the right.
- Double-click Turn On Virtualization Based Security, select Disabled, and select OK.
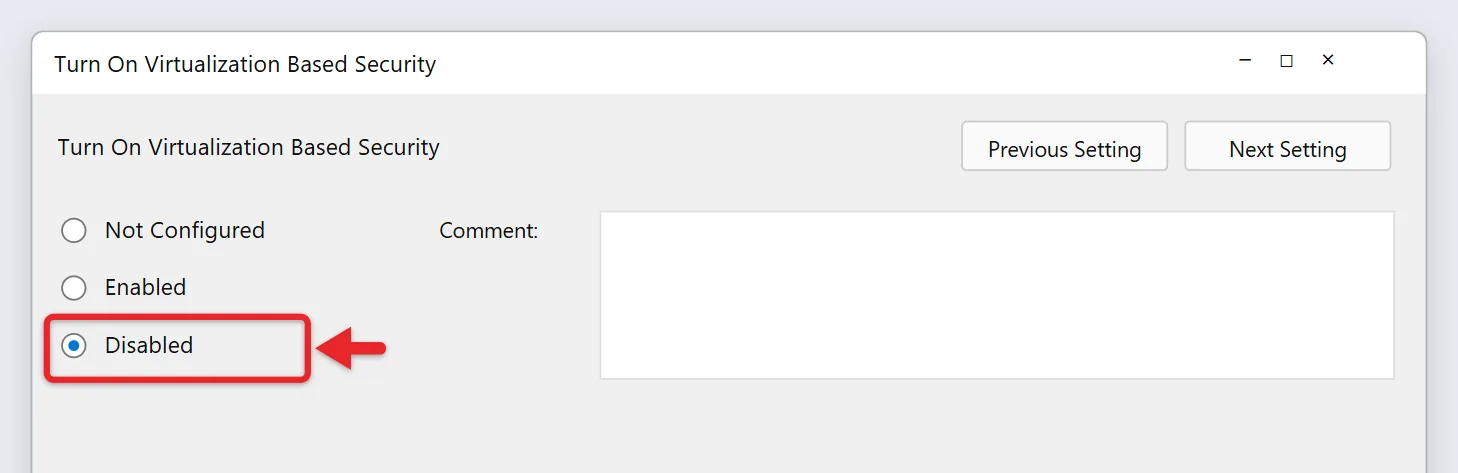
- Restart the PC and run the check above again.
This policy controls VBS as a whole, so setting it to Disabled can switch off other protections too. On a domain-joined PC, the administrator must change the controlling GPO, because the domain policy replaces a local edit. Don’t install an unofficial Group Policy Editor to get around a missing one.
Method 2: Registry (No UEFI Lock and No Group Policy)
Microsoft says registry edits are enough when Credential Guard was not turned on with a UEFI lock or by Group Policy, including when Windows turned it on by default.
- Open Start, search regedit, and open Registry Editor. Select Yes at the permission prompt.
- Go to
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Lsa. Set the REG_DWORD value LsaCfgFlags to 0. If it’s missing, create a DWORD (32-bit) value with that name. - Go to
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\DeviceGuard. Create the DeviceGuard key if it’s missing, and set LsaCfgFlags to 0 there as well. Change nothing else.
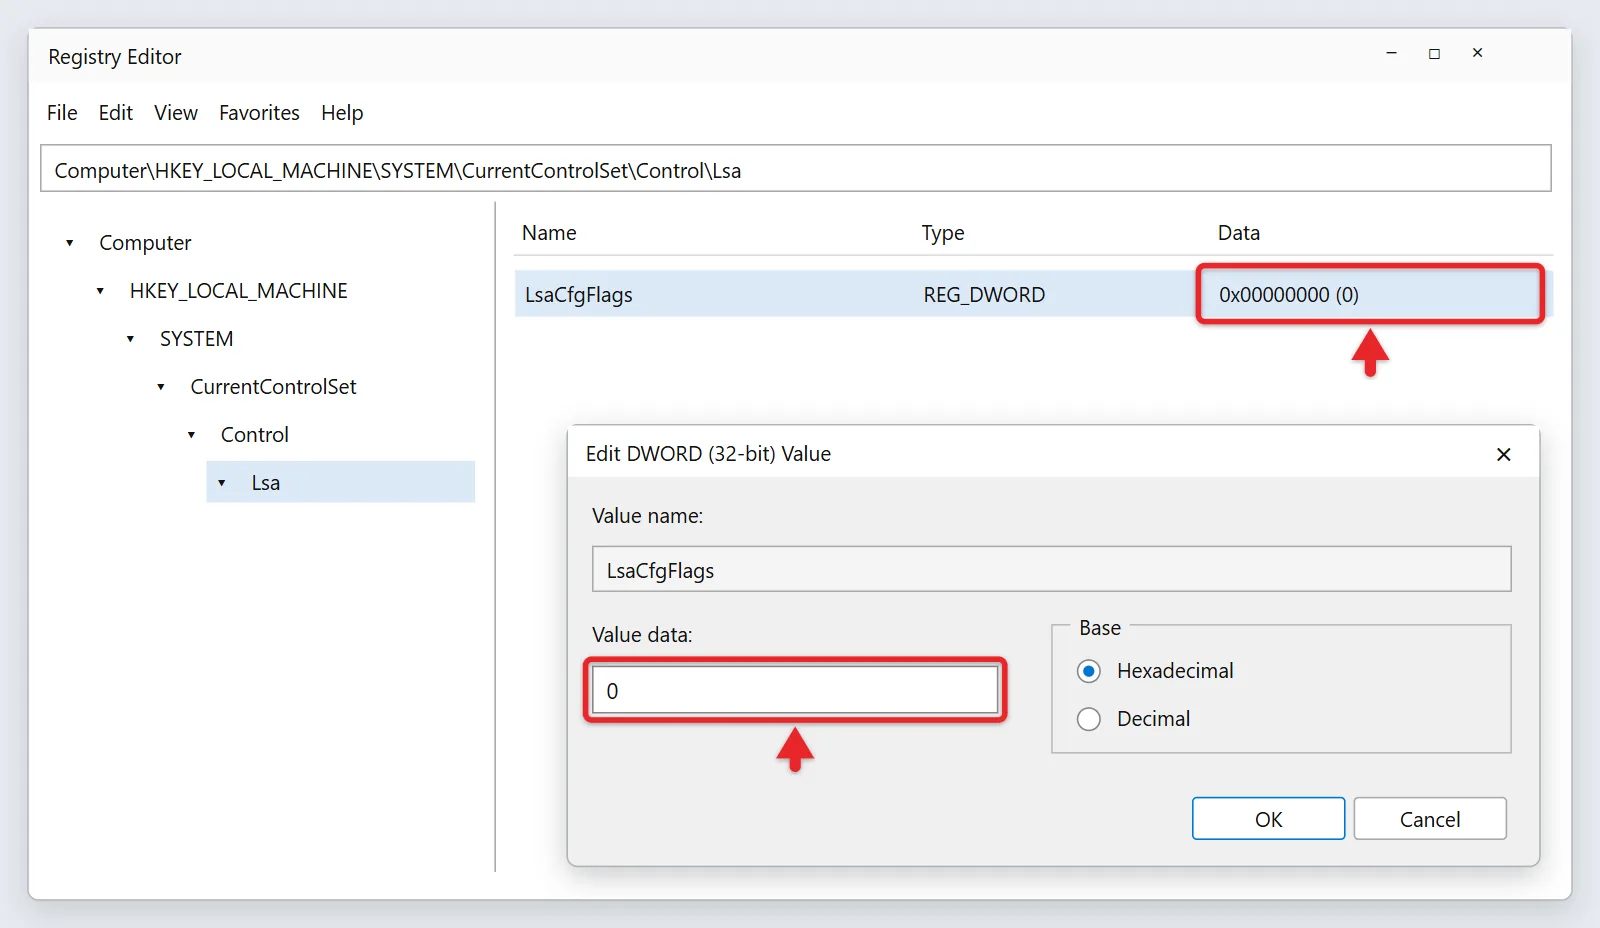
- Close Registry Editor, save your work, and restart. Repeat the running-state check.
Set the values to 0; Microsoft notes that deleting them may not disable Credential Guard. If Registry Editor says access is denied, the PC is probably managed, so ask your IT administrator.
Intune-Managed PCs
On Intune-managed PCs, a local edit won’t stick. The administrator sets Device Guard > Credential Guard > Disabled, or LsaCfgFlags = 0 in the DeviceGuard policy reference, which defines 1 as enabled with UEFI lock and 2 as enabled without lock.
If Credential Guard Has a UEFI Lock
Microsoft notes that a UEFI lock stores the setting in firmware, so registry and policy changes alone can’t remove it. Its Disable Credential Guard with UEFI lock procedure requires someone at the PC to confirm a prompt during startup; have your administrator follow it exactly. Default enablement uses no lock, so most PCs won’t have one.
Confirm It’s Off and Retest the App
After restarting, run the System Information or PowerShell check again. Credential Guard should no longer be listed as running. Then retest the app that failed; if the error remains, Credential Guard probably wasn’t the cause, and you should turn it back on.
Troubleshooting
- It’s still running after a restart: a domain GPO or Intune policy may be applying it again, or it has a UEFI lock. Check with the administrator.
- You deleted the values: add them back and set them to 0, as Microsoft requires.
- Saved Remote Desktop credentials fail: Microsoft says Windows credentials saved by the Remote Desktop client can’t be sent with Credential Guard on, and you’ll see “Logon attempt failed.” Typing the password each time still works.
- Don’t rely on Task Manager: Microsoft says checking for the LsaIso.exe process isn’t a reliable test.
Turn Credential Guard Back On
Restore protection when the exception ends, with the same method you used, then restart and confirm it’s running.
- Group Policy: set Turn On Virtualization Based Security to Enabled and choose Enabled without lock under Credential Guard Configuration. Microsoft recommends this option if you want to be able to turn it off remotely later.
- Registry: under the Lsa key, set LsaCfgFlags to 2 (enabled without lock). Microsoft’s enable settings also list EnableVirtualizationBasedSecurity = 1 and RequirePlatformSecurityFeatures = 1 under
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\DeviceGuard. For the LsaCfgFlags value under the Policies DeviceGuard key, restore the value you recorded, or delete it if it didn’t exist before. - Backup: in Registry Editor, File > Import restores your exported keys. An import merges saved values; it doesn’t remove values added later.
Frequently Asked Questions
Why might it affect Wi-Fi, VPN, or saved sign-ins?
Microsoft’s known-issues guide says connections using older protocols such as MS-CHAPv2 or NTLMv1 lose single sign-on and ask for your password each time. It recommends certificate-based authentication, such as EAP-TLS, instead.
Can I allow just one application?
No. Microsoft says it’s either on or off, with no per-app policy, and turning it off leaves stored domain credentials open to theft.
Will turning it off fix every virtualization error?
No. Credential Guard, memory integrity, VBS and Hyper-V are different features. Check which one the error names.
Matthew Burleigh is the founder, head writer, and editor of Solve Your Tech, which he launched in 2012. He has written technology tutorials since 2008 and worked in IT since 2003, including small-business support, IT management, and consulting. He holds Bachelor’s and Master’s degrees in Computer Science from Arizona State University.
Matthew writes practical guides for Windows, iPhone and iPad, Microsoft Office, Outlook, Google apps, and Android. Solve Your Tech’s guides are checked step by step against the device or app maker’s own documentation and tested on his own devices whenever he has the hardware or software, with clear steps, sources, and update dates.
Read more about Matthew and how Solve Your Tech writes and updates its guides, or report a correction.