Your PC restarted on its own overnight, an app keeps closing without warning, or a support agent asks for an event ID, and Event Viewer is where Windows writes down what happened. To use Event Viewer in Windows 11, right-click Start, select Event Viewer, expand Windows Logs, and pick System or Application. Select an entry to read it, and use Filter Current Log to show only errors.
This covers Windows 11 Home and Pro, versions 24H2 and 25H2.
Five Ways to Open Event Viewer
Use whichever is quickest for you. They all open the same tool. You can read most logs with a standard account; the Security log and clearing logs need an administrator.
- Start search: select Start, type Event Viewer, and open it from the results.
- Quick Link menu: right-click the Start button (or press Windows key + X) and choose Event Viewer.
- Run box: press Windows key + R, type
eventvwr.msc, and press Enter. - Computer Management: open Computer Management from the Windows key + X menu, then expand System Tools > Event Viewer. This puts Event Viewer next to Device Manager and Disk Management in one window.
- Terminal: type
eventvwrin Terminal, PowerShell or Command Prompt and press Enter.
Event Viewer is usually also listed in the Windows Tools folder (Start > All apps > Windows Tools).
The first time it opens, Event Viewer may take a few seconds while it reads the logs. That’s normal.
What You See When It Opens
The window has three columns.
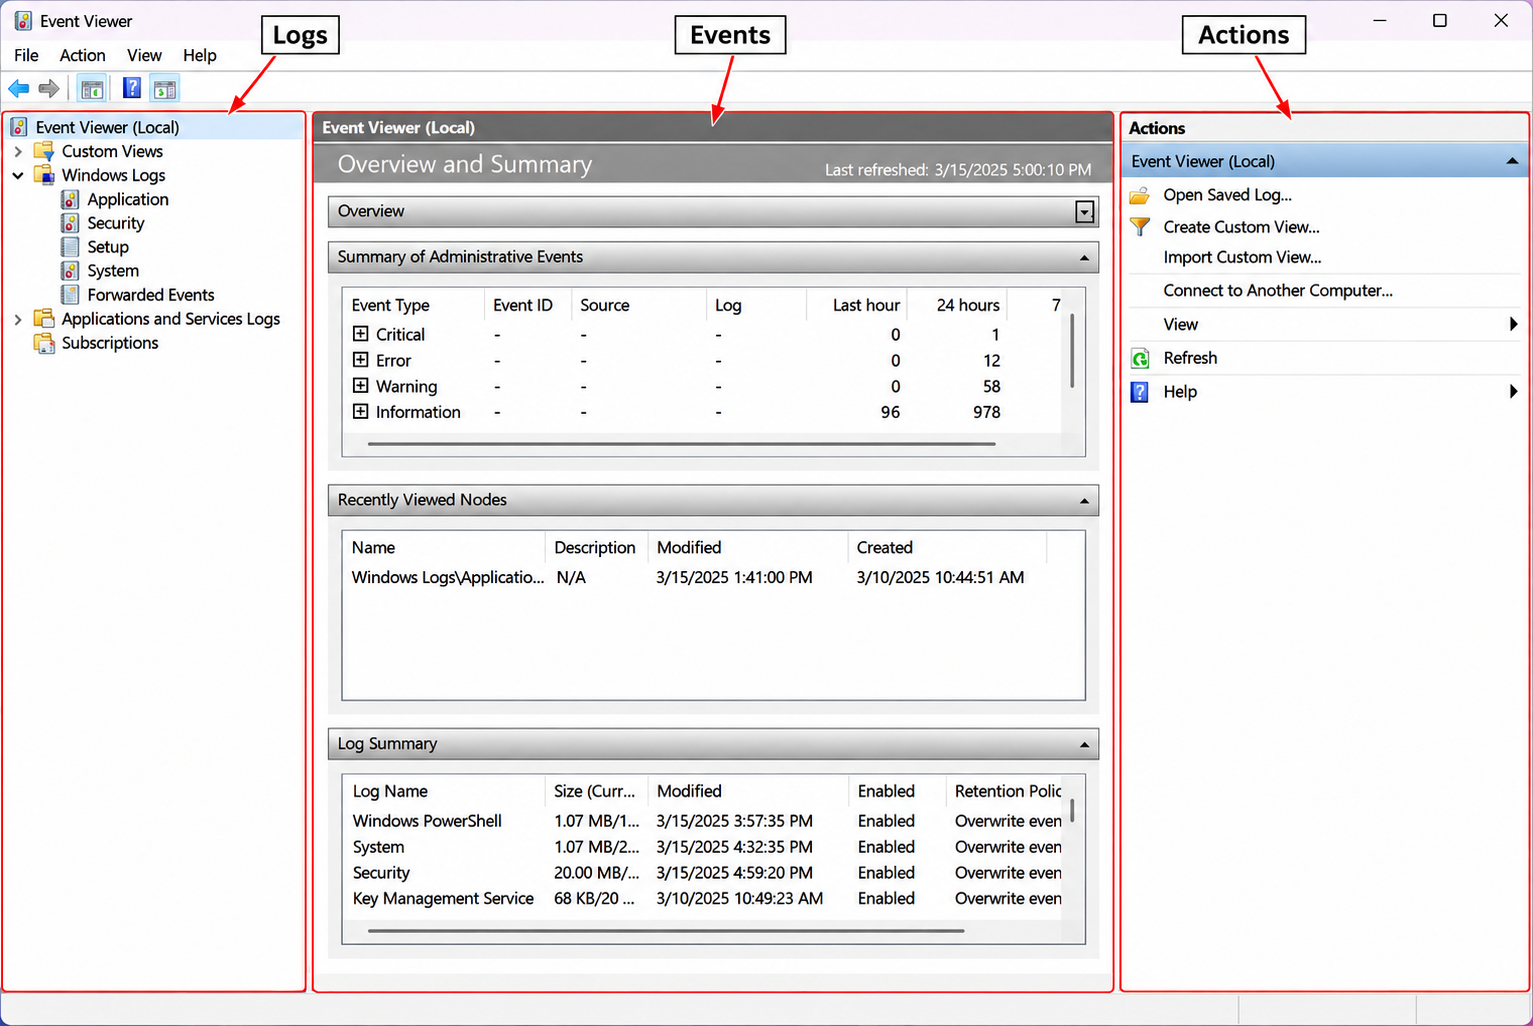
- Left (console tree): the folders of logs. This is where you choose what to look at.
- Middle: when you first open Event Viewer it shows an Overview and Summary, with counts of Critical, Error and Warning events over the last hour, day and week. Once you select a log, the middle becomes a list of events on top and a preview of the selected event underneath.
- Right (Actions pane): the commands for whatever is selected, such as Filter Current Log, Find, Create Custom View and Save All Events As.
If the Actions pane is missing, the window may be too narrow, or it was turned off. Widen the window, or use the View menu to show it again.
Which Log to Look In
Event Viewer holds dozens of logs, but most everyday questions are answered in a handful of them.
| Log | Where it is | What goes in it |
|---|---|---|
| Administrative Events | Custom Views | Critical, Error and Warning events from all administrative logs, gathered in one place |
| Application | Windows Logs | Events from apps and programs, such as an app crashing |
| Security | Windows Logs | Sign-in attempts and other audited actions (administrator needed) |
| Setup | Windows Logs | Events from installing Windows features and updates |
| System | Windows Logs | Windows itself, drivers and services: startups, shutdowns, device problems |
| Forwarded Events | Windows Logs | Events sent from other PCs; empty on most home PCs |
| Applications and Services Logs | Left pane | Detailed logs for individual Windows features and some apps, under Microsoft > Windows |
A simple rule: if an app misbehaved, look in Application. If the whole PC restarted, froze or lost a device, look in System. The Administrative Events custom view is a good starting point when you don’t know which.
What the Levels Mean
Every event has a level, shown with an icon in the list.
- Critical: a serious failure, such as Windows restarting without shutting down cleanly.
- Error: a significant problem, such as a service failing to start or an app crashing.
- Warning: something that isn’t necessarily a problem now but could become one.
- Information: a normal operation that worked, such as a service starting.
- Audit Success and Audit Failure: security events, such as a successful or failed sign-in. These appear in the Security log.
Microsoft’s descriptions of the basic event types cover Error, Warning, Information and the two audit types; Critical is the extra level newer logs use for the most serious failures.
Lots of red is normal
Open the System log on a perfectly healthy PC and you’ll still find errors and warnings. A service that took a little longer to start, a driver that tried a device that wasn’t plugged in, an app that couldn’t reach a server for a moment: Windows logs all of it. An error only matters if it lines up with a problem you actually noticed, at the time you noticed it, and especially if it repeats. Don’t try to fix every red entry.
Read a Single Event
Select an event in the list and its details appear in the lower half of the middle pane. Double-click it to open the same details in a separate window.
The General tab shows the message in plain text plus these fields:
- Log Name and Source: which log it’s in and which program, driver or service wrote it.
- Event ID: a number the source uses for this kind of event. The same ID from a different source means something else, so always note the ID and the Source together.
- Level: Critical, Error, Warning or Information.
- Logged: the date and time. Match this to when your problem happened.
- User and Computer: the account and PC involved.
The Details tab shows the raw data behind the event, either in a Friendly View or as XML. Support staff sometimes ask for values from here, such as an error code. To copy an event, select it and press Ctrl + C, then paste it into an email or chat.
Filter, Find and Save a Custom View
A busy log has thousands of entries, so filtering is the skill that makes Event Viewer useful.
Filter the current log
- Select a log in the left pane, such as Windows Logs > System.
- In the Actions pane, select Filter Current Log.
- Choose a time range in the Logged list, such as Last 24 hours.
- Check the levels you want, for example Critical and Error.
- Optionally, pick an Event source or type event IDs in the box (separate several with commas, such as
41,6008).
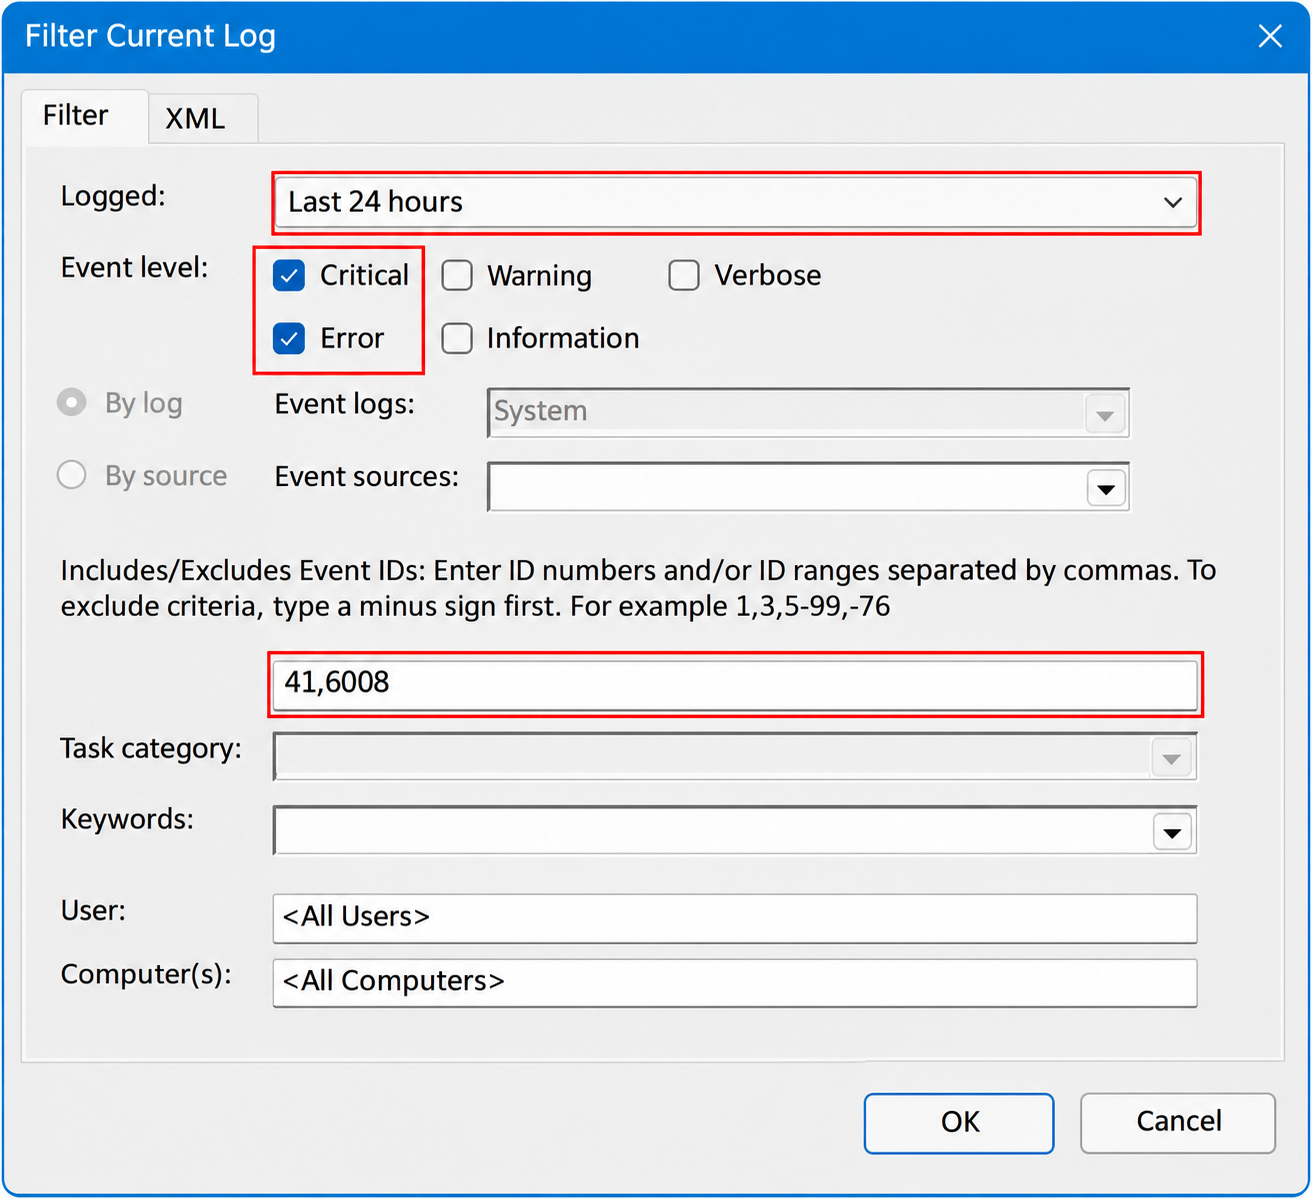
- Select OK. The list now shows only matching events, and the top of the list says it’s filtered.
To see everything again, select Clear Filter in the Actions pane.
Search for a word
Select Find in the Actions pane and type part of a message, such as an app name. Event Viewer jumps to the next event that contains it. Find searches the log you’re looking at, so filter first if the log is large.
Save the filter as a custom view
If you check the same thing often, save it.
- Select Create Custom View in the Actions pane.
- Set the time range and levels, then choose By log and pick one or more logs (for example System and Application).
- Select OK, give the view a name such as Errors this week, and select OK again.
Your view appears under Custom Views in the left pane and updates every time you open it.
Event IDs Worth Knowing
A few events come up again and again when people investigate restarts. Microsoft’s article on Event ID 41 and unexpected restarts describes these, all in the System log:
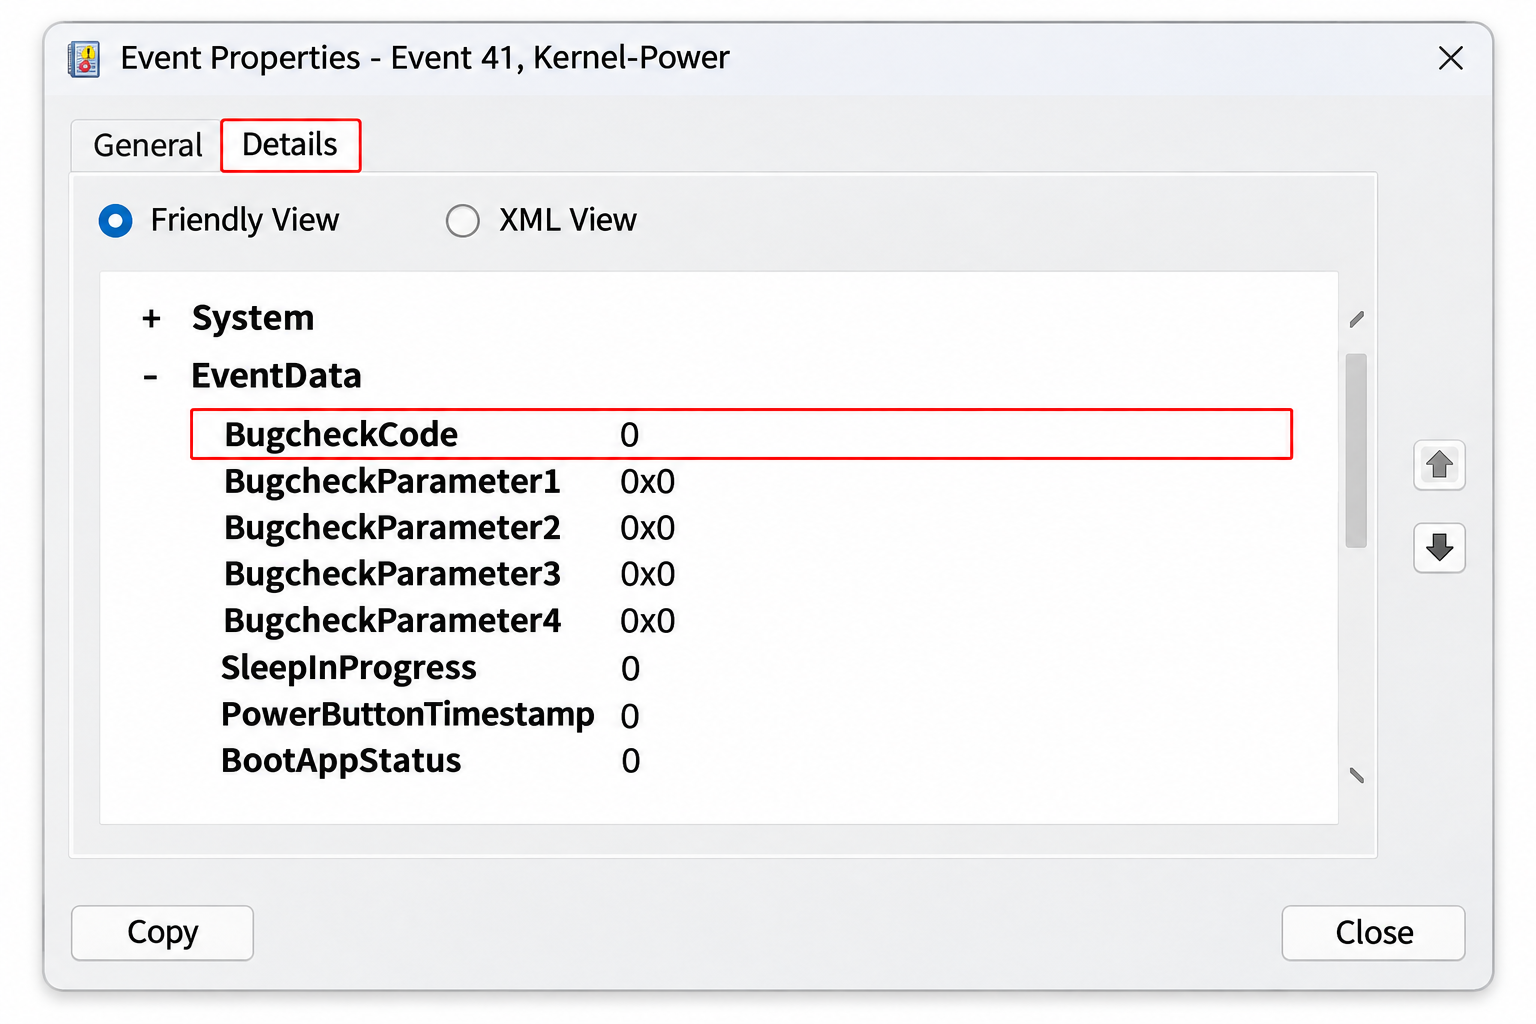
- Event ID 41, source Kernel-Power, level Critical: “The system has rebooted without cleanly shutting down first.” Windows writes it at the next startup after the PC stopped responding, crashed or lost power. By itself it doesn’t say why.
- Event ID 6008: the previous shutdown was unexpected.
- Event ID 1074: a user or an app started the shutdown or restart. The message usually names the process, which is handy when an update or a program restarted the PC overnight.
Event 41 has a BugcheckCode field on the Details tab. If it’s not zero, Windows hit a Stop error (a blue screen) and the code points to the cause. If it’s zero, no Stop error was recorded: the PC may have lost power or have a power supply or battery problem (a zero can also appear if no memory dump file is set up). A nonzero PowerButtonTimestamp means the power button was held down to turn it off. For blue screens and app crashes in more depth, the walkthrough on checking crash logs in Windows 11 lists more IDs and what to do with them.
To look up any other event, search for its Event ID together with its Source on Microsoft’s support sites.
Save, Clear and Resize Logs
Save events to send to someone
- Select the log or custom view (filtered, if you only want part of it).
- Select Save All Events As in the Actions pane. If a filter is on, the option may read Save Filtered Log File As.
- Choose the .evtx format, pick a location and a name, and select Save. If asked about display information, include it so the file reads correctly on another PC.
Anyone with Event Viewer can open an .evtx file with Action > Open Saved Log. A support agent can read your events exactly as you see them.
Clear a log
Clearing deletes every event in that log, and you can’t undo it. It doesn’t fix anything; it just gives you a clean slate so new events are easy to spot. To clear one, right-click the log and select Clear Log, then choose Save and Clear to keep a copy first. You need administrator rights.
Change how much a log keeps
Windows keeps each log to a maximum size and overwrites the oldest events when it’s full. To keep more history, right-click a log, select Properties, and raise Maximum log size (KB). Microsoft’s page on setting the maximum log file size notes it needs administrator rights and is set in multiples of 64 KB.
Run a Task When an Event Happens
Event Viewer can start an action whenever a specific event is logged. Right-click an event and choose Attach Task To This Event. A wizard asks for a name, then what to do, such as starting a program or script. Windows saves it as a task in Task Scheduler, where you can edit or delete it later.
A practical example: a home media PC keeps dropping its network connection. You attach a task to the network adapter’s error event that runs a small script to write the time to a text file, then compare the times with when the drops happen. Use it sparingly; a task attached to a common event runs very often.
Easier and Faster Alternatives
Reliability Monitor
Reliability Monitor reads the same logs and turns them into a timeline, with red X marks for days with crashes or failed updates. Select Start, type reliability, and open View reliability history. It’s the friendlier view when you just want to know what went wrong this week. For more on combining it with Event Viewer, see how to check error logs on Windows 11.
PowerShell and wevtutil
If you prefer commands, PowerShell’s Get-WinEvent reads the same logs. These show the 20 newest System events, then only Kernel-Power 41 events:
Get-WinEvent -LogName System -MaxEvents 20
Get-WinEvent -FilterHashtable @{ LogName='System'; Id=41 }
The built-in wevtutil command can list logs, query them and export them, which is handy for scripts:
wevtutil el
wevtutil qe Application /c:3 /rd:true /f:text
wevtutil epl System C:\Logs\system.evtx
The first lists every log name, the second shows the three newest Application events as text, and the third exports the System log to a file.
Next time something odd happens, write down the time, then open Event Viewer and filter the System or Application log to that hour. One matching event with its ID and Source is usually all a support agent or a search needs.
Reading Event Viewer Without Panicking
Why can’t I find events from a few months ago?
Each log has a maximum size, and once it’s full Windows overwrites the oldest events. A busy System log may only reach back a few weeks. Raise the maximum size in the log’s Properties if you need a longer history, and save important events to an .evtx file.
Does Event Viewer slow down my PC?
No. Windows writes the logs whether or not you open Event Viewer, and the logs have size limits so they don’t fill your drive.
Can I see who signed in to my PC?
On your own PC, an administrator can check the Security log for sign-in events (Audit Success and Audit Failure). Filter it by date to narrow things down.

Matthew Burleigh is the founder, head writer, and editor of Solve Your Tech, which he launched in 2012. He has written technology tutorials since 2008 and worked in IT since 2003, including small-business support, IT management, and consulting. He holds Bachelor’s and Master’s degrees in Computer Science from Arizona State University.
Matthew writes practical guides for Windows, iPhone and iPad, Microsoft Office, Outlook, Google apps, and Android. Solve Your Tech’s guides are checked step by step against the device or app maker’s own documentation and tested on his own devices whenever he has the hardware or software, with clear steps, sources, and update dates.
Read more about Matthew and how Solve Your Tech writes and updates its guides, or report a correction.