To enable TPM on a supported PC, first check its status with tpm.msc. If it is disabled, enable the existing TPM in your computer’s firmware settings, save the change, and verify the result in Windows. Windows 11 requires TPM 2.0; a firmware switch cannot add missing hardware or guarantee that an older TPM can be upgraded.
The steps below cover a physical PC running Windows 11 or Windows 10, including a Windows 10 PC being checked for a Windows 11 upgrade. Firmware menus differ by model. Use the computer or motherboard maker’s instructions for the actual switch.
Check Whether TPM Is Already Enabled
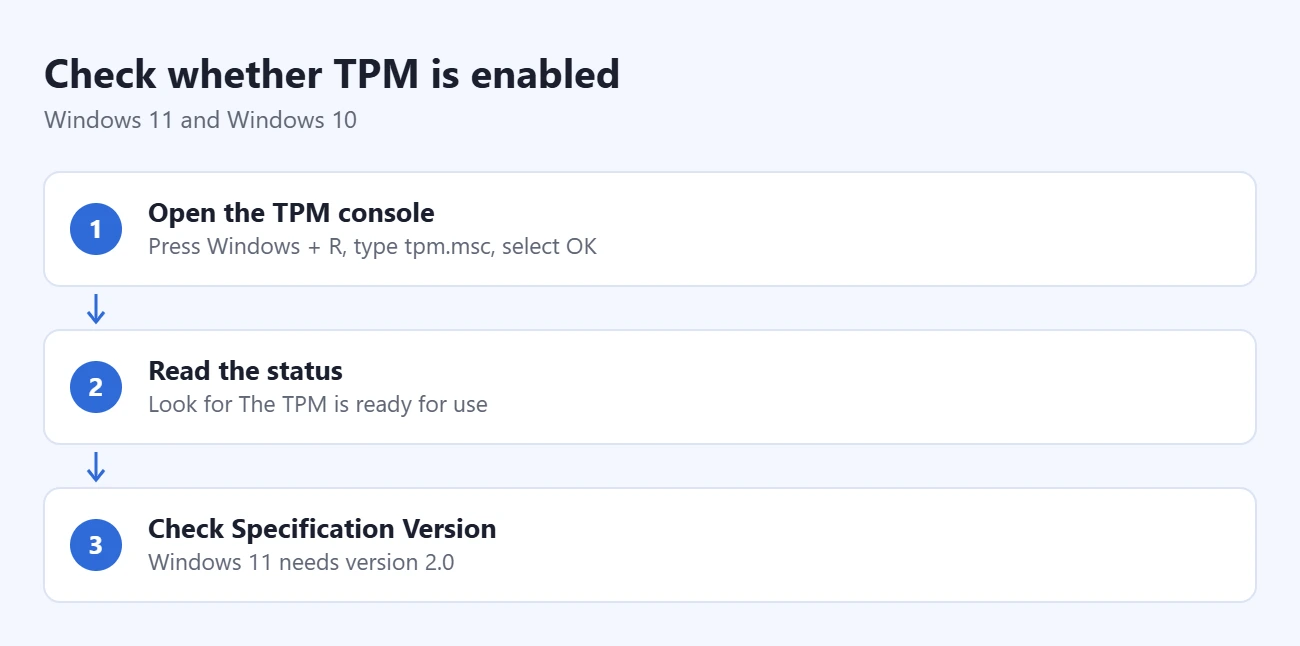
- Press Windows + R, type tpm.msc, and select OK.
- Read the status. If the TPM is ready for use, look under TPM Manufacturer Information for Specification Version.
- For Windows 11, verify that the version is 2.0. If it is ready and already 2.0, you do not need to enable it again.
A message saying a compatible TPM cannot be found can mean it is disabled; it does not alone prove that the computer lacks one. Microsoft’s TPM enabling guide explains these checks and common firmware labels.
Prepare Before Changing Firmware
Have a usable recovery method for encrypted data before changing TPM settings. Microsoft’s TPM troubleshooting documentation warns that switching between TPM implementations can trigger BitLocker recovery, and clearing a TPM can lose keys and access to protected data. Enabling an existing TPM is different from clearing it. Do not choose Clear TPM, reset its keys, or switch between firmware and discrete TPM as part of this basic guide.
If BitLocker or Device Encryption protects your drive, locate the recovery key before restarting. Microsoft’s recovery-key guide covers Microsoft accounts, work or school accounts, printouts, and saved USB copies. A recovery key is a 48-digit number; a key ID helps identify the right one. Store it where you can retrieve it if this PC cannot open Windows.
Save your work and back up important files. For an organization-managed computer, ask IT to handle the change. If the firmware demands an administrator password you do not know, stop and contact its owner or administrator.
Open the Firmware Settings
- On Windows 11, open Settings > System > Recovery. Under Advanced startup, select Restart now. Microsoft’s firmware-access instructions document this route.
- On Windows 10, use Settings > Update & Security > Recovery, then Restart now under Advanced startup.
- After the restart, choose Troubleshoot > Advanced options > UEFI Firmware Settings > Restart. Expect the manufacturer’s setup screen instead of the Windows desktop.
If UEFI Firmware Settings is absent, check the manufacturer’s startup-key instructions. For example, Dell’s TPM guide uses F2 at the Dell logo. That key is a Dell example, not a universal shortcut. Do not change Legacy/CSM boot mode, storage settings, or partition layout just to make this menu appear.
Enable the Existing TPM and Verify It
- Locate the model’s TPM control. Menus may use Security, Advanced, or Trusted Computing. Labels can include Security Device Support, TPM State, Intel PTT, or AMD fTPM.
- Follow the maker’s instructions to turn that existing TPM control on. Record its previous setting. Read any warning carefully; if the action would clear keys or change TPM type, stop and get model-specific guidance.
- Use the firmware’s documented save-and-exit command. Allow the PC to restart, then sign in to Windows.
- Run tpm.msc again. Confirm that the TPM is ready for use and check its specification version. For Windows 11 compatibility, it must show 2.0.
Dell documents Intel PTT and AMD fTPM as firmware implementations, so a separate add-in chip is not always necessary. Its menus and available controls still depend on the model. Windows normally initializes an available TPM automatically; creating a TPM owner password is not a required step in this guide.
If the Check Still Fails
- No TPM control: Check the exact model’s manual and support information. Buy no add-in module until the manufacturer confirms compatibility.
- Version 1.2: That does not meet Windows 11’s TPM 2.0 requirement. For continued Windows 10 use, check the requirements of the particular security feature you need. A supported version upgrade is model-dependent; enabling TPM does not itself convert 1.2 to 2.0.
- Enabled but not detected: Record the Windows message and firmware setting, then use manufacturer support. Do not clear TPM or install firmware from an unrelated model as a generic fix.
- Windows 11 upgrade still blocked: TPM is only one requirement. Check the other compatibility results rather than repeating the firmware change. If the processor is what fails, read about your options when Windows 11 does not support your CPU.
For locating model and version information, see our BIOS and UEFI settings guides. Start with the Windows status check, change only the documented TPM control if necessary, and confirm the result afterward.
Matthew Burleigh is the founder, head writer, and editor of Solve Your Tech, which he launched in 2012. He has written technology tutorials since 2008 and worked in IT since 2003, including small-business support, IT management, and consulting. He holds Bachelor’s and Master’s degrees in Computer Science from Arizona State University.
Matthew writes practical guides for Windows, iPhone and iPad, Microsoft Office, Outlook, Google apps, and Android. Solve Your Tech’s guides are tested on current devices or checked against official product documentation, with clear steps, sources, and update dates.
Read more about Matthew and how Solve Your Tech writes and updates its guides, or report a correction.